· Goher K · Web Development & DevOps · 8 min read
How to Clear Laravel Cache via a Secure URL Route Without Server SSH
Learn how to clear all Laravel caches via a permanent, secure URL route using environment tokens and Artisan calls without terminal or SSH access on any server.
Managing Laravel applications across staging and production environments frequently requires clearing application caches whenever environment variables are updated, Blade templates are modified, or routing definitions change. Under standard server management practices, developers execute terminal commands such as php artisan optimize:clear directly over SSH. However, in shared hosting environments (such as cPanel, DirectAdmin, or Plesk), client staging servers, or enterprise configurations where SSH terminal access is restricted, manual cache clearing often turns into a tedious, time-consuming chore.
For developers operating on budget shared hosting platforms (such as Namecheap, Hostinger, GoDaddy, or Bluehost), this limitation is especially painful. Most shared hosting plans disable SSH terminal access entirely by default, jail the CLI shell, or lock command-line tools behind costly hosting upgrades. Whenever code is uploaded or synced via FTP, Git, or cPanel File Manager, Laravel continues to serve stale cached configurations, old routes, and outdated Blade views. Without terminal access, developers are forced to manually traverse deep file paths (bootstrap/cache/ and storage/framework/views/) or open slow technical support tickets just to flush a single change.
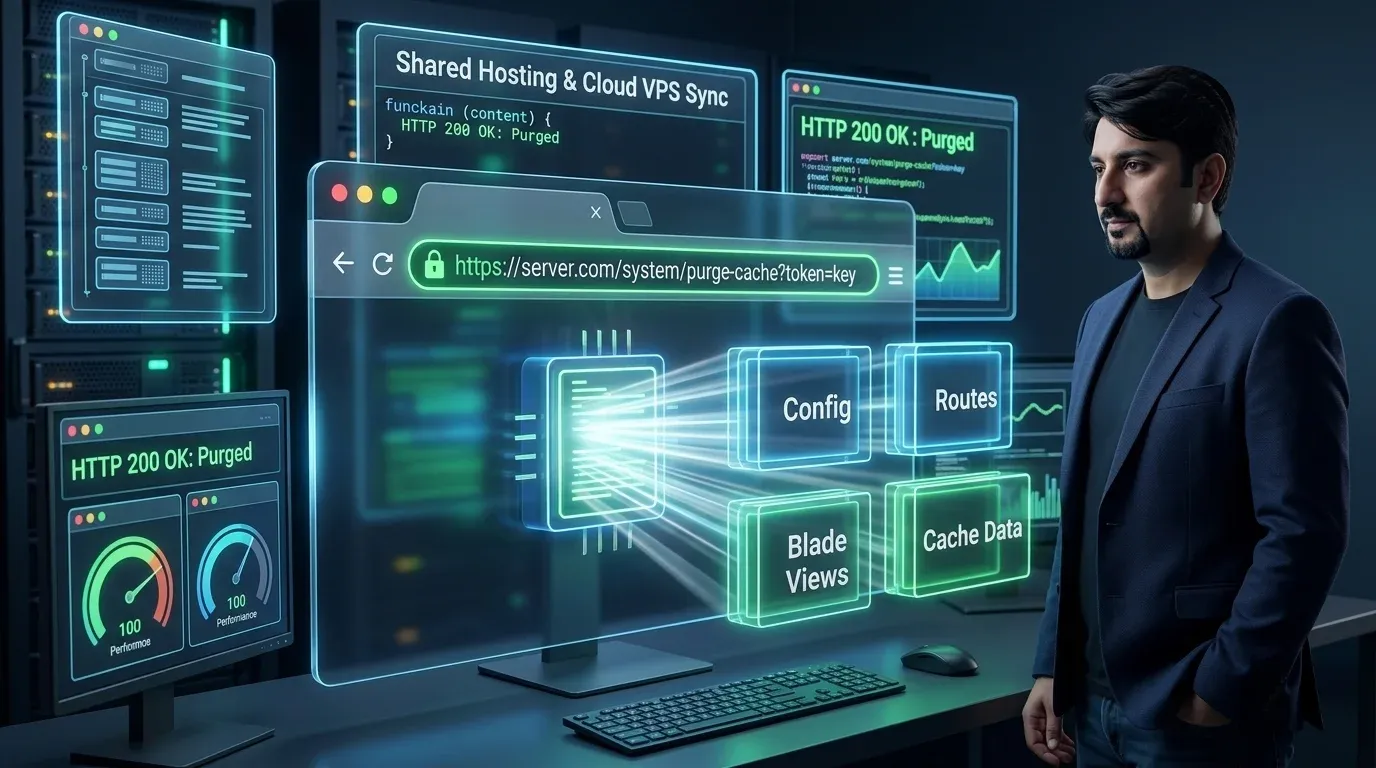
By implementing a permanent, authenticated web route, developers can trigger complete Artisan cache flushes via browser URL in a fraction of a second. This bridges the gap for shared hosting completely, bringing full Artisan console power directly to your browser without needing SSH privileges.
This guide provides a robust, production-grade architectural pattern to configure an authenticated Laravel cache-clearing endpoint that eliminates terminal dependency while ensuring strict protection against unauthorized execution.
The Hidden Danger of Naive Cache-Clearing Routes
A common anti-pattern found on developer forums suggests adding an open route directly inside routes/web.php:
// ❌ INSECURE ANTI-PATTERN: DO NOT USE IN PRODUCTION
Route::get('/clear-cache', function () {
    Artisan::call('optimize:clear');
    return 'Cache cleared!';
});
Deploying an unprotected route like this introduces serious operational vulnerabilities:
- Denial-of-Service & Cache Stampedes: Web crawlers, vulnerability bots, and search indexers will repeatedly hit this URL, wiping production caches and forcing the server to recompile templates and configurations continuously.
- Timing-Attack Vulnerabilities: Basic token checks comparing query strings with standard
===operators leak execution timing differences, opening the door to character-by-character timing attacks. - Cached Configuration Failure: Calling
env('CACHE_KEY')directly within route closures fails silently and returnsnullwhenever configuration caching (php artisan config:cache) is enabled.
A production-grade implementation requires four defensive measures: Rate limiting, timing-safe hash comparisons, proper configuration registration, and terminal response capture.
Step 1: Define the Secret Authentication Token
Generate a cryptographically secure 64-character token on your local machine using PHP’s native random bytes generator:
php -r "echo bin2hex(random_bytes(32)) . PHP_EOL;"Add this token to your server’s .env file:
# Secure Laravel Cache Clear Token
CACHE_CLEAR_TOKEN=f7b4c92a18e3d64098521bcde431fae807192834e56712398450abcd1234ef56
Next, map this variable inside your application configuration file. Open config/app.php and append the token entry to the configuration array:
// Inside config/app.php
'cache_clear_token' => env('CACHE_CLEAR_TOKEN'),
Critical Architecture Rule: Never invoke the
env()helper inside controllers, middleware, or routes. Oncephp artisan config:cacheis compiled, Laravel bypasses the.envfile entirely. Accessing the key throughconfig('app.cache_clear_token')guarantees consistent availability regardless of caching state.
Step 2: Create the Dedicated Cache Manager Controller
Encapsulating maintenance routines inside a dedicated controller keeps route files clean, enables structured error logging, and standardizes JSON responses.
Create the controller via Artisan:
php artisan make:controller System/CacheManagerControllerAdd the following production-ready implementation inside app/Http/Controllers/System/CacheManagerController.php:
<?php

namespace App\Http\Controllers\System;

use App\Http\Controllers\Controller;
use Illuminate\Http\JsonResponse;
use Illuminate\Http\Request;
use Illuminate\Support\Facades\Artisan;
use Illuminate\Support\Facades\Log;

class CacheManagerController extends Controller
{
    /**
     * Clear all application and framework caches securely.
     */
    public function clear(Request $request, string $token): JsonResponse
    {
        $configuredToken = (string) config('app.cache_clear_token');

        // Verify token presence and validate using constant-time comparison
        if (empty($configuredToken) || !hash_equals($configuredToken, (string) $token)) {
            Log::warning('Unauthorized cache clear attempt intercepted', [
                'ip' => $request->ip(),
                'user_agent' => $request->userAgent(),
            ]);

            return response()->json([
                'status' => 'error',
                'message' => 'Unauthorized action. Invalid security token.',
            ], 403);
        }

        $outputs = [];

        // 1. Clear application data cache
        Artisan::call('cache:clear');
        $outputs['cache'] = trim(Artisan::output());

        // 2. Clear compiled route cache
        Artisan::call('route:clear');
        $outputs['routes'] = trim(Artisan::output());

        // 3. Clear compiled configuration cache
        Artisan::call('config:clear');
        $outputs['config'] = trim(Artisan::output());

        // 4. Clear compiled Blade view templates
        Artisan::call('view:clear');
        $outputs['views'] = trim(Artisan::output());

        // 5. Clear compiled event discovery cache
        Artisan::call('event:clear');
        $outputs['events'] = trim(Artisan::output());

        // 6. Execute full optimize sweep
        Artisan::call('optimize:clear');
        $outputs['optimize'] = trim(Artisan::output());

        Log::info('System cache purged successfully via secure URL route', [
            'ip' => $request->ip(),
        ]);

        return response()->json([
            'status' => 'success',
            'message' => 'All Laravel caches have been successfully cleared.',
            'timestamp' => now()->toIso8601String(),
            'diagnostics' => $outputs,
        ], 200);
    }
}
Step 3: Register the Throttled Maintenance Route
In routes/web.php, register the URL route protected with Laravel’s built-in throttle middleware to prevent brute-force token enumeration:
use App\Http\Controllers\System\CacheManagerController;
use Illuminate\Support\Facades\Route;

// Protected maintenance endpoint restricted to 5 requests per minute
Route::get('/system/purge-cache/{token}', [CacheManagerController::class, 'clear'])
    ->middleware('throttle:5,1')
    ->name('system.purge-cache');
This syntax is identical and fully supported across Laravel 10, Laravel 11, and Laravel 12.
Step 4: Testing and Validating Cache Purges
To clear application caches, navigate to the endpoint in your browser or trigger it from your terminal:
curl -X GET "https://yourdomain.com/system/purge-cache/f7b4c92a18e3d64098521bcde431fae807192834e56712398450abcd1234ef56"Expected JSON Diagnostic Response
When the security token matches, the controller executes the Artisan commands and returns a 200 OK response with exact command outputs:
{
  "status": "success",
  "message": "All Laravel caches have been successfully cleared.",
  "timestamp": "2026-10-22T03:15:00+00:00",
  "diagnostics": {
    "cache": "Application cache cleared successfully.",
    "routes": "Route cache cleared successfully.",
    "config": "Configuration cache cleared successfully.",
    "views": "Compiled views cleared successfully.",
    "events": "Cached events cleared successfully.",
    "optimize": "Caches cleared successfully!"
  }
}
If an incorrect token is provided, the request fails with a 403 Forbidden response:
{
  "status": "error",
  "message": "Unauthorized action. Invalid security token."
}
Breakdown of Cleared Laravel Cache Types
Understanding the specific role of each cache layer helps developers pinpoint deployment anomalies:
| Cache Component | Artisan Command | Storage Location | Operational Impact |
|---|---|---|---|
| Application Cache | cache:clear | storage/framework/cache/data or Redis | Removes application query results, session tags, and transient key-value data. |
| Config Cache | config:clear | bootstrap/cache/config.php | Reloads newly added .env settings and modified configuration arrays. |
| Route Cache | route:clear | bootstrap/cache/routes-v7.php | Rebinds modified URLs, controller actions, and endpoint middlewares. |
| Compiled Views | view:clear | storage/framework/views/*.php | Forces the Blade engine to recompile fresh HTML components and layout blocks. |
| Event Discovery | event:clear | bootstrap/cache/events.php | Refreshes event-to-listener auto-discovery mapping tables. |
| Optimize Sweep | optimize:clear | Framework-wide | Multi-directory umbrella command flushing all above layers in one unified pass. |
Production Best Practices and Security Hardening
- Re-cache for High-Traffic Applications:
Clearing caches leaves routes and configs uncompiled. On high-traffic production platforms, immediately follow a purge withphp artisan config:cacheandphp artisan route:cacheto maintain optimal TTFB latency. - Restrict by IP Whitelist:
For mission-critical production systems, restrict execution to trusted corporate or VPN IP addresses:if (!in_array($request->ip(), ['203.0.113.195', '198.51.100.42'])) { abort(403, 'IP unauthorized.'); } - Inspect Application Logs:
Regularly reviewstorage/logs/laravel.logto track cache clearing frequency and identify potential unauthorized URL probing attempts.
Frequently Asked Questions
Is it safe to keep a cache clear route permanently in Laravel?
Yes, provided the route is guarded with a high-entropy secret token (32+ bytes), uses constant-time string comparison (`hash_equals`), and is restricted by rate-limiting middleware (`throttle:5,1`). Never deploy an open, unauthenticated cache clear route in a production environment.
Why does env() return null when I check my token?
Once you run `php artisan config:cache`, Laravel bundles all configuration files into a single cached file and stops reading the raw `.env` file during request lifecycles. Always register your token in `config/app.php` and access it using `config('app.cache_clear_token')` instead of calling `env()` directly.
What is the difference between cache:clear and optimize:clear?
`php artisan cache:clear` only flushes the application data cache (e.g., Redis, Memcached, or file-based data). `php artisan optimize:clear` is an umbrella command that cleans compiled views, cached routes, cached configuration, event discovery files, and application data cache simultaneously.
Can I clear Laravel cache via cPanel File Manager without URL routes?
Yes. In cPanel File Manager, you can manually delete `config.php` and `routes.php` inside `bootstrap/cache/`, as well as cached files inside `storage/framework/cache/data/` and `storage/framework/views/`. However, setting up a secure URL route is far faster and avoids accidental deletion of critical framework files.
Does this secure cache clearing URL work on cPanel and shared hosting?
Yes, absolutely. This solution was engineered specifically for shared hosting environments (including cPanel, Plesk, Hostinger, Namecheap, and Bluehost) where terminal SSH access is unavailable or disabled. Because the route runs through standard HTTP/HTTPS web workers handled by Apache or Nginx, PHP executes Artisan::call() with native web permissions, completely bypassing the need for a command-line interface.
Need Help Scaling Your Laravel Architecture?
If your enterprise application requires advanced CI/CD pipelines, high-availability Redis clustering, or database query optimization, our engineering team can audit and accelerate your infrastructure.