Emergency IT Support & Administration
Google Workspace Quick Fix: Emergency DNS, Domain & Admin Solutions
Surgical Remediation for Critical Tenancy Roadblocks.Direct, senior-architect troubleshooting for mission-critical Google Workspace friction points. From zero-downtime primary domain switches and secondary domain alias routing to SPF, DKIM, and DMARC deliverability repairs, we resolve single-issue administrative challenges rapidly without lengthy sales cycles or bloated agency retainers.
What is Google Workspace Quick Fix?
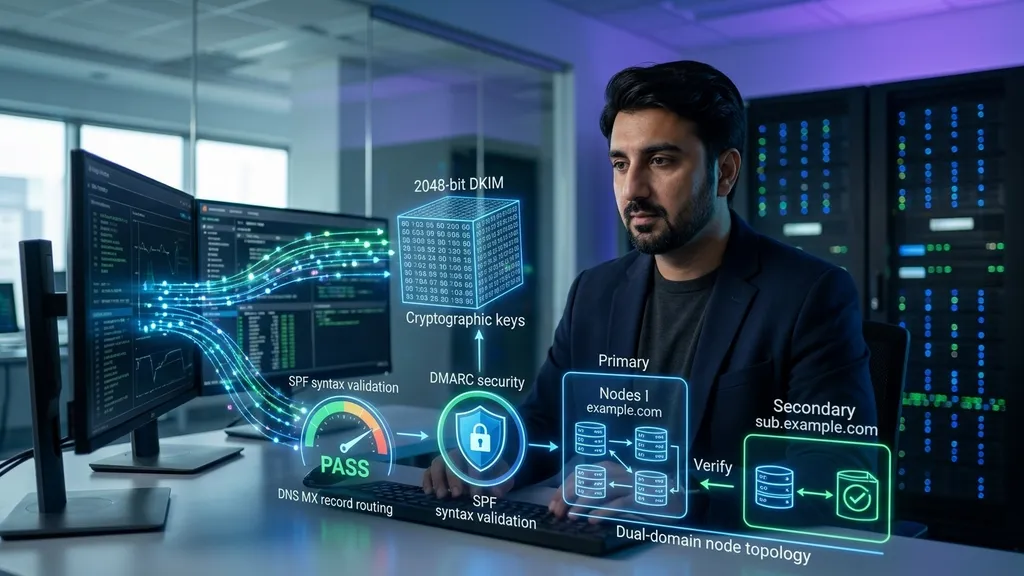
Google Workspace Quick Fix is a targeted, rapid-response IT engineering service designed to resolve mission-critical Google Workspace administrative roadblocks without multi-week consulting retainers. Whether your organization faces email deliverability failures under Google and Yahoo bulk-sender rules, needs a zero-downtime primary domain switch, requires secondary domain alias routing, or must contain an emergency account compromise, a senior solutions architect directly diagnoses and resolves the issue. All work is executed under strict least-privilege delegated access with zero-downtime guarantees and complete credential protection.
Engineered for Zero-Downtime Cloud Operations
Direct technical intervention for businesses that cannot afford email bouncebacks, compromised user accounts, or days in standard support ticket queues.
The Cloud Administration Dilemma
Why Standard Support Queues & Generic IT Providers Fail at Google Workspace
Standard helpdesks and freelance contractors frequently lack deep DNS authority knowledge, leading to bounced invoices, broken routing, and security exposures.
Broken Email Deliverability & Silent Spam Flags
When transactional invoices or client emails land in spam, generic support desks advise waiting for propagation instead of diagnosing missing DKIM keys or SPF syntax errors.
Primary Domain Rebranding Blackouts
Switching a primary domain inside Google Admin without setting up alias preservation and pre-verifying MX records causes catastrophic inbound email bounces across the entire team.
Exceeded SPF 10-Lookup PermErrors
Connecting CRMs, marketing platforms, and ticketing tools pushes your SPF string beyond the strict RFC 7208 10-lookup limit, causing global receiving mailservers to drop your messages.
Compromised Accounts & Delayed Containment
Waiting days in vendor ticketing queues while an employee account is hijacked allows attackers to exfiltrate proprietary data, harvest client lists, and establish persistent OAuth backdoors.
Targeted Technical Fixes
What's Included in Your Workspace Quick Fix
Nine surgical deliverables that restore administrative order, email deliverability, and domain authority to your Google Workspace environment.
Switch Primary Workspace Domain
Migrate your core Google Workspace tenancy to a new primary domain with zero mail downtime. We manage domain verification, alias preservation, and secondary routing.
Secondary Domain & Subdomain Setup
Add and verify secondary domains or subdomains for subsidiary brands. We configure MX mailflow, user aliases, and distinct sending identities under unified governance.
Email Deliverability (SPF, DKIM, DMARC)
Eliminate spam flags and email bouncebacks. We audit existing DNS zones, generate 2048-bit DKIM keys, resolve SPF 10-lookup limits, and enforce strict DMARC alignment.
Account Compromise & Hijack Recovery
Rapid response for compromised user or administrator accounts. We execute immediate session revocation, password resets, rogue OAuth token auditing, and 2FA enforcement.
Suspended Admin & User Restoration
Regain access to suspended, disabled, or locked Google Workspace administrator accounts. We navigate Google verification protocols and resolve organizational security lockouts.
Offboarding & Data Archival Transfers
Securely offboard departing staff without data loss. We transfer Google Drive files, export historical Gmail archives to Vault, reallocate licenses, and close access vectors.
Gmail Routing & Compliance Rules
Build custom inbound/outbound email routing rules, dual-delivery splits, content compliance filters, automated company disclaimers, and data loss prevention guardrails.
Collaborative Inboxes & Delegation
Configure zero-license shared inboxes via Google Groups for Business or browser-native Gmail Email Delegation, enabling team collaboration without credential sharing.
Google Sites Custom Domain Mapping
Link and activate your custom root and www domains to internal or public Google Sites. We resolve CNAME records, HTTPS/SSL propagation delays, and apex 301 redirects.
Diagnostic Intake & Delegated Access → Authoritative DNS & Mailflow Audit → Surgical Admin Console Remediation → Live Inbound/Outbound Deliverability Validation → Secure Access Revocation.
“Enterprise cloud tenancy issues should never result in customer communication blackouts. When your primary domain changes or emails flag as spam, you need surgical architectural intervention, not a multi-day support ticket queue.”— Goher K, Principal Solutions Architect at iGoher
Delivery Models Compared
Generic Ticket Queues & Freelancers vs. iGoher Quick Fix
See the practical difference between waiting on generic helpdesks and partnering with a dedicated enterprise cloud solutions architect.
| Operational Factor | Generic Support Queues & FreelancersTier-1 queues, trial-and-error edits & handoffs | iGoher Workspace Quick FixDirect senior architect & surgical executionRecommended |
|---|---|---|
| Response & TriageTime elapsed from initial incident intake to active remediation | 24 to 72 hour ticket wait times with canned automated responses | Direct architect intake with emergency triage response under 2 hours |
| Security & Access ModelMethod used to authenticate and execute administrator changes | Demands shared master super-admin passwords or unvetted tools | Strict zero-trust delegated access; zero master password sharing required |
| Mailflow DowntimeImpact on inbound customer inquiries during domain alterations | DNS changes often cause dropped inbound customer emails and bounced messages | Zero-downtime staged migration protocol with preserved alias routing |
| Email AuthenticationLevel of cryptographic compliance with Google and Yahoo rules | Basic SPF txt records without DKIM or strict DMARC alignment | Flawless 2048-bit DKIM, SPF flattening (< 10 lookups), and strict DMARC enforcement |
| Diagnostic DepthMethodology used to uncover underlying cloud infrastructure faults | Treats symptoms superficially (e.g., re-sending emails, resetting browsers) | Surgical root-cause audit across authoritative DNS zones and Google core policies |
| AccountabilityOwnership of the final resolution and verification testing | Finger-pointing between domain registrar, web host, and Google support | Single senior solutions architect directly accountable from intake to sign-off |
Transparent Scope
Micro-Fix Agility vs. Full Enterprise Tenant Migrations
Understanding the exact boundaries of our Google Workspace Quick Fix service ensures your team receives immediate, surgical relief with zero scope confusion.
Designed for Immediate Operational Relief
When your outbound invoices are flagged as spam, or your corporate rebranding requires promoting a new primary domain without dropping a single customer inquiry, you do not need a three-week consulting discovery phase. You need an experienced IT architect who diagnoses the exact DNS syntax error, validates Google Admin Console policies, and executes the fix cleanly.
What Quick Fix Covers
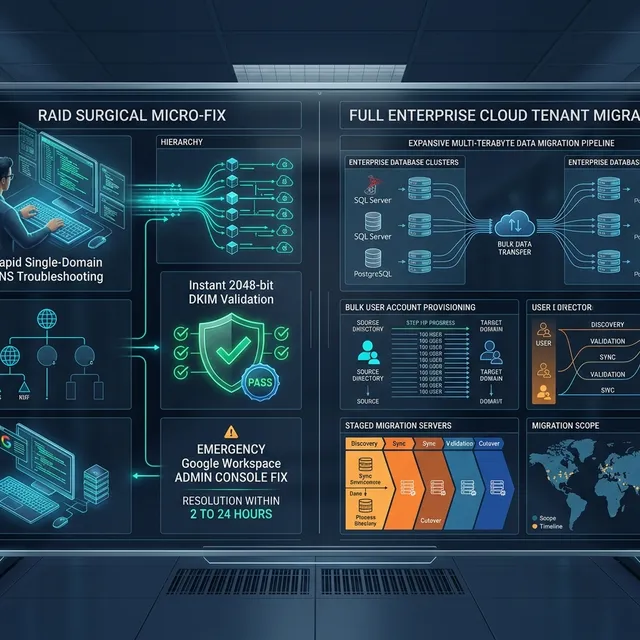
Emergency troubleshooting and surgical configuration of single administrative roadblocks: DNS deliverability repairs, primary/secondary domain transitions, compromised account lockdown, user offboarding, and group routing. Fast turnaround under 2 to 48 hours.
What Requires Full Enterprise Scope
Cross-tenant data migrations involving thousands of mailboxes, multi-terabyte SharePoint-to-Drive restructuring, complex SSO/SAML federations with Okta or Azure AD, or ongoing outsourced helpdesk retainers. These are handled as structured architectural projects.
Least-Privilege Security Guarantee
You never share your personal or master super-admin password. All work is conducted using scoped, delegated administrative roles or time-bound collaborative sessions that you can instantly revoke.
Structured Delivery
The 4-Stage Rapid Resolution Protocol
Every Google Workspace quick fix follows a structured, four-phase sequence to guarantee zero disruption and complete data security.
- 1
Phase 1: Scoped Intake & Delegated Access
You share the exact symptoms, error logs, and target domain names. We establish secure, time-bound delegated administrative access via the Google Admin Console without requesting master passwords or root credentials.
- 2
Phase 2: Technical Diagnostic & DNS Zone Audit
We inspect authoritative DNS zones (Cloudflare, AWS Route 53, GoDaddy, etc.), audit MX and TXT record syntax, analyze message headers, test SPF lookup depth, and identify underlying configuration conflicts.
- 3
Phase 3: Surgical Configuration & Staged Rollout
We implement the exact configuration fixes inside Google Admin Console and authoritative DNS, establishing 2048-bit DKIM keys, aligning DMARC policies, and configuring routing rules under strict rollback contingencies.
- 4
Phase 4: Live Verification & Access Revocation
We execute live inbound and outbound message delivery tests across major destination providers (Gmail, Microsoft 365, Yahoo), confirm SPF/DKIM/DMARC pass states, provide sign-off documentation, and confirm access removal.
Architectural Rigor
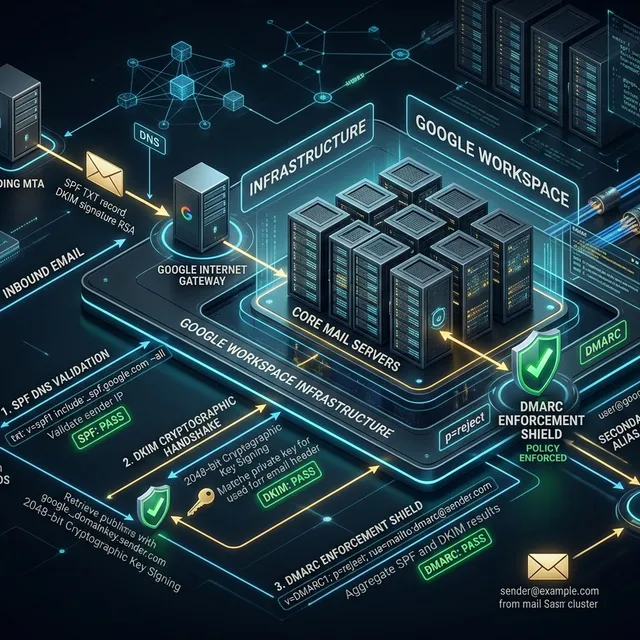
Engineering Flawless Email Authentication & Domain Integrity
Why modern Google Workspace administration requires strict compliance with 2024+ security standards and zero-trust operational protocols.
Mandatory 2024+ Bulk Sender Alignment
Google and Yahoo enforce strict email delivery thresholds: mandatory SPF, DKIM, and DMARC alignment, alongside a reported spam rate strictly below 0.10%. Misconfigured records result in immediate domain-wide throttling or junk folder placement.
SPF 10-DNS-Lookup Limit Resolution
Adding third-party sending services (CRM, billing, marketing automation) frequently exceeds the RFC 7208 10-lookup limit, causing catastrophic validation failures. We audit, streamline, and flatten SPF records to guarantee 100% pass rates.
2048-bit Cryptographic DKIM Signing
Many legacy domains still rely on outdated 1024-bit DKIM keys or unaligned default selectors. We generate and activate full 2048-bit RSA keys directly in your Google Admin Console to safeguard brand identity against spoofing.
Phased DMARC Policy Enforcement
Moving safely from p=none (monitoring) to p=quarantine and p=reject requires analyzing aggregate RUA telemetry reports. We ensure legitimate transaction streams are authenticated before blocking malicious spoofers.
Quick Fix Scopes
Choose the Targeted Quick Fix Scope for Your Roadblock
Three structured micro-engagements designed to resolve your Google Workspace administrative challenges—from deliverability repairs to zero-downtime domain transitions.
DNS & Email Deliverability Fix
Focus: Eliminate spam flags and restore flawless inbox delivery for transactional and business emails.
• Full DNS zone audit across authoritative nameservers
• 2048-bit DKIM cryptographic key generation & activation
• SPF string flattening & 10-lookup limit resolution
• DMARC policy record deployment & alignment validation
• Google & Yahoo 2024+ bulk-sender compliance testing
• Live inbound/outbound delivery verification report
Most Requested Fix
Domain Transition & Alias Architecture
Focus: Rebrand or expand your domain footprint with zero mailflow disruption or bounced messages.
• Zero-downtime primary domain switch & promotion
• Secondary domain & subdomain TXT ownership verification
• Seamless user mailbox rebranding & alias preservation
• Inbound/outbound email dual-delivery & routing rules
• Google Sites custom domain CNAME & SSL mapping
• Google Groups collaborative inbox configuration
Zero-Downtime Guarantee
Emergency Incident & Security Containment
Focus: Rapid triage and administrative containment for compromised, suspended, or departing accounts.
• Global session cookie revocation & emergency password reset
• Malicious third-party OAuth app auditing & token purge
• Investigation of unauthorized Gmail delegation backdoors
• 20-day deleted account, Gmail, and Google Drive recovery
• Suspended administrator account verification & unlock
• Hardware-backed 2-Step Verification (2SV) enforcement
Emergency Triage < 2h
A Clear, Transparent, and Secure Remediation Process
We believe enterprise cloud administration requires absolute transparency, strict security controls, and zero administrative ambiguity:
- Zero Password Sharing: You never disclose your super administrator master password. All work is conducted using scoped, time-bound delegated custom roles or screen-share collaborative sessions that you control.
- Zero-Downtime Mailflow Guarantee: For primary domain switches and secondary routing, all DNS records and alias bridges are pre-configured before the domain cutover, ensuring not a single customer message is bounced or dropped.
- Complete Documentation & Immediate Revocation: Upon project verification, you receive a full audit trail detailing every DNS record, Google Admin setting, and security rule modified, followed by immediate delegated access removal.
Core Tenancy Glossary
Essential Concepts in Google Workspace Administration
Clear technical definitions of key infrastructure components involved in resolving Google Workspace tenancy challenges.
- Primary Domain Switch
- The administrative procedure of elevating a secondary domain to the default identity space within Google Workspace, rebranding user login handles while maintaining historical message archives.
- Secondary Domain vs. Domain Alias
- A secondary domain allows users to have distinct primary email addresses with separate sending identities, whereas a domain alias provides mirror addresses that route automatically to primary mailboxes.
- SPF 10-Lookup Limit (RFC 7208)
- The technical constraint preventing SPF records from requiring more than 10 recursive DNS queries during evaluation. Exceeding this limit results in a permanent PermError validation failure.
- 2048-bit Cryptographic DKIM
- An asymmetric public-key signature standard that cryptographically signs outbound emails to verify sender authenticity and prevent domain spoofing across modern receiving mail exchangers.
- DMARC Policy Progression
- The methodical process of advancing a domain's email authentication policy from p=none (monitoring) to p=quarantine and p=reject based on real-world aggregate RUA telemetry reports.
- Scoped Delegated Administration
- A zero-trust access methodology where external specialists are granted temporary, granular privileges limited strictly to the required organizational units and DNS zones without master credentials.
Quick Fix Inquiries
Frequently Asked Questions About Google Workspace Quick Fix
Direct answers regarding Google Workspace emergency troubleshooting, domain transitions, deliverability fixes, and security protocols.
How quickly can an emergency Google Workspace issue be diagnosed and resolved?
Most single-issue quick fixes—such as broken SPF/DKIM records, secondary domain TXT verification failures, or user suspension lockouts—are triaged within 2 hours of receiving scoped delegated access. Standard DNS propagation for newly deployed MX or DMARC records typically settles across global recursive resolvers in 2 to 24 hours. Emergency incident containment (such as session revocation and compromised account lockdown) begins immediately upon initial intake.
Can switching my primary Google Workspace domain cause email loss or downtime?
Not when executed under a phased migration protocol. We ensure zero mail downtime by first pre-configuring all MX and security records on the target domain, setting up bidirectional routing rules, and adding the new domain as a secondary domain or domain alias prior to promotion. Once Google confirms domain ownership and email routing is validated, the primary domain switch is triggered with existing user handles preserved as aliases so that zero inbound messages are bounced.
What is the technical difference between a Domain Alias and a Secondary Domain in Google Workspace?
A Domain Alias automatically assigns every user in your organization a mirror email address on the secondary domain at zero extra license cost (e.g., user@domain-b.com routes to user@domain-a.com). In contrast, a Secondary Domain functions as a distinct identity space within the same admin console: users can have their primary mailbox located entirely on domain-b.com with discrete signatures and routing policies, while sharing internal Drive storage and admin governance.
Why are our outgoing company emails suddenly landing in Gmail and Outlook spam folders?
Under the strict bulk-sender requirements enforced by Google and Yahoo, domains sending email must have strict SPF alignment, valid 2048-bit DKIM cryptographic signatures, and a published DMARC policy with matching From headers. Furthermore, exceeding the 10-DNS-lookup limit in your SPF string causes a permanent validation error (PermError), causing receiving servers to treat your legitimate mail as unauthenticated spoofing. We audit, flatten, and cryptographically align your DNS stack to restore pristine sender reputation.
How do you access our Google Workspace environment without compromising root security?
We adhere to strict zero-trust security standards. You never share your super administrator master credentials or personal passwords. Instead, we guide you through assigning a scoped, time-bound delegated custom administrator role inside your Google Admin Console (Account > Admin Roles), limited strictly to the organizational units, domains, or user settings requiring remediation. Access is revoked immediately upon project verification and sign-off.
What should we do immediately if an employee account or administrator is compromised?
Immediate containment is critical. First, log into the Google Admin Console and trigger a global session revocation (Security > Sign-in cookies reset) to terminate all active desktop and mobile web sessions. Next, reset the account password, revoke all granted OAuth third-party app tokens, inspect Gmail auto-forwarding rules or unauthorized delegation permissions that attackers frequently plant as persistence backdoors, and enforce hardware-backed 2-Step Verification (2SV).
Can you recover emails or Drive files from an account that was accidentally deleted?
Google enforces a strict 20-day recovery window for deleted accounts. If the account was deleted within the last 20 days, we can restore the user, their historical Gmail archive, and their Google Drive assets directly from the Admin Console. Beyond 20 days, data is permanently purged from Google core infrastructure unless your organization had active Google Vault retention holds or external cloud backups running prior to the deletion event.
Do you work directly on our DNS registrar (Cloudflare, GoDaddy, Namecheap, Route 53)?
Yes. Google Workspace configuration requires coordinated updates between the Google Admin Console and your authoritative DNS management zone. Whether your nameservers reside on Cloudflare, AWS Route 53, Google Cloud DNS, GoDaddy, Namecheap, or cPanel, we can either implement the precise TXT, MX, CNAME, and DMARC records via delegated access or provide exact, copy-paste syntactical strings with zero ambiguity.
Let’s Connect
Resolve Your Google Workspace Issue Today
Describe your domain, current symptoms, or configuration roadblocks below. We provide immediate architectural assessment and rapid triage within 2 hours.